RE Toolkit (5/5): malware triage and patch diffing — capa, FLOSS, YARA-X, BinDiff, ghidriff
TL;DR
Automated triage answers 'what can this file do' in minutes with capa, FLOSS and YARA-X. Patch diffing with ghidriff (one command, Ghidra), BinDiff or Diaphora shows which functions a patch changed. Keep learning with mytechnotalent/Reverse-Engineering and nightmare.
Two questions come up constantly in security work: "What can this unknown file do?" and "What did the patch that just shipped fix?". Answering them by reading every function in Ghidra takes days. The final part of the RE Toolkit series covers repos that automate both: capa, FLOSS and YARA for fast triage, BinDiff, Diaphora and ghidriff for patch diffing, plus three learning repos to keep going.
Part 1: fast triage
| Repo | Answers the question | Stars · License |
|---|---|---|
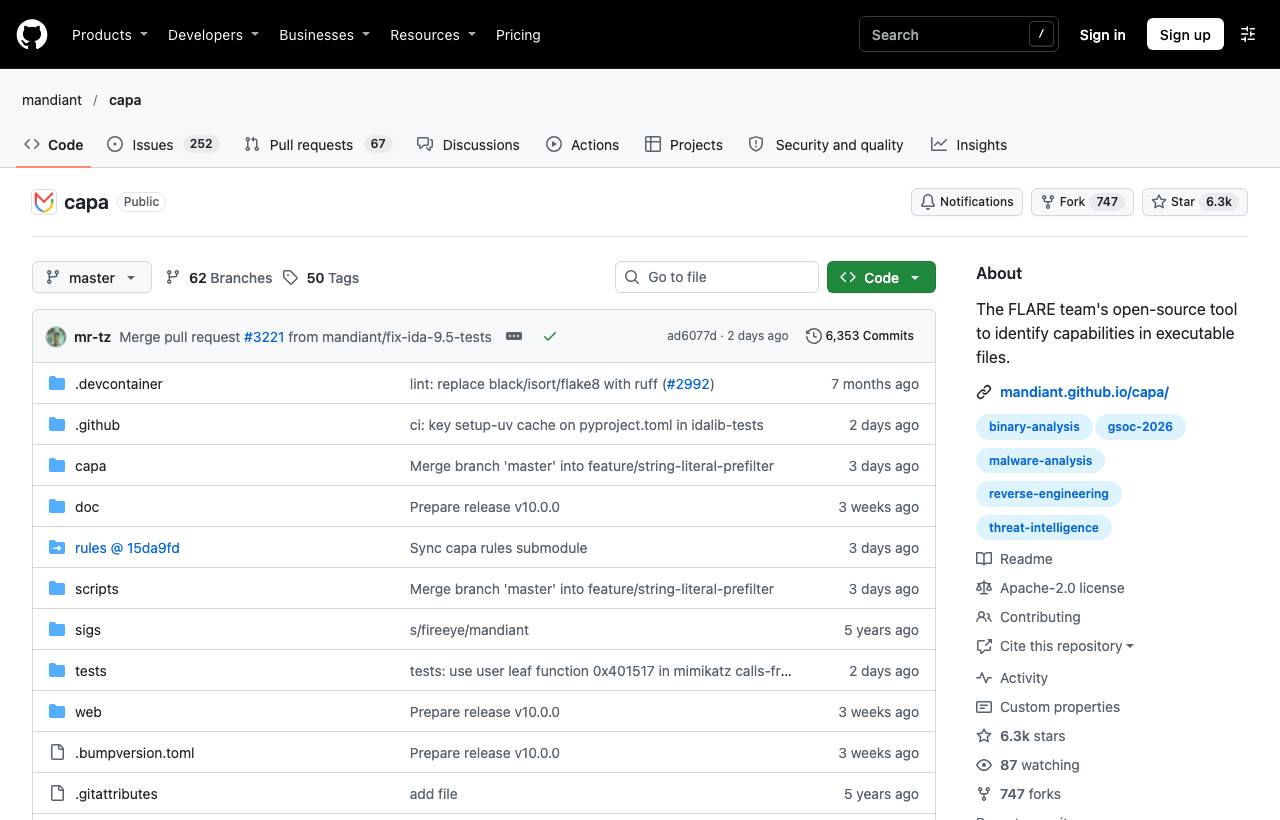
| mandiant/capa | What capabilities does this program have (network, persistence, crypto…)? | ~6.3k · Apache-2.0 |
| mandiant/flare-floss | Which strings are hidden (encrypted, stack-built) where strings can't see them? | ~4.2k · Apache-2.0 |
| VirusTotal/yara-x / yara | Which files match known patterns? (YARA-X is the Rust rewrite) | ~1.4k / ~10k · BSD-3-Clause |
capa: capabilities instead of signatures
capa takes a PE, ELF, .NET module, shellcode or sandbox report and matches it against the community rule set (the capa-rules repo) to list capabilities mapped to MITRE ATT&CK. Results like "send HTTP request", "create service" or "execute shell command" tell you which functions to open first.
capa sample.exe          # ATT&CK table + capability list
capa -v sample.exe       # verbose: where each capability lives
Results can be explored visually in capa Explorer Web or loaded into IDA/Ghidra to jump to the relevant functions.
FLOSS and YARA
FLOSS emulates decoding routines to recover hidden strings, often revealing C2 URLs, mutex names and registry keys. YARA turns those findings into rules to scan thousands of other files:
floss sample.exe

rule Suspicious_Downloader {
  strings:
    $api = "URLDownloadToFileA" ascii
    $cmd = "cmd.exe /c" ascii nocase
  condition:
    uint16(0) == 0x5A4D and all of them
}

yr scan rules.yar ./samples/     # YARA-X
Part 2: patch diffing
When a vendor ships a security fix without details, diffing the binary before and after shows exactly which functions changed. Defenders use it to judge urgency and write detections; developers use it to check that a third-party library's patch really matches its changelog.
| Repo | Runs on | Strengths | Stars · License |
|---|---|---|---|
| google/bindiff | IDA, Ghidra, Binary Ninja (via BinExport) | Industry standard, open-sourced by Google, graph comparison UI | ~3.2k · Apache-2.0 |
| joxeankoret/diaphora | IDA | Many matching heuristics, compares decompiled pseudocode too | ~4.5k · AGPL-3.0 |
| clearbluejar/ghidriff | Ghidra, command line | One command, Markdown/JSON/HTML output, easy to automate | ~0.8k · GPL-3.0 |
ghidriff: a patch diff in one command
ghidriff uses free Ghidra to find added, deleted and modified functions, plus "meta diffs" of strings and callers/callees. Per its README, once Ghidra analysis is done it can diff the entire Windows kernel in under a minute.
pip install ghidriff        # requires an installed Ghidra
ghidriff old/driver.sys new/driver.sys
# or with Docker:
docker run -it --rm -v $(pwd)/ghidriffs:/ghidriffs \
  ghcr.io/clearbluejar/ghidriff:latest ghidriffs/old.sys ghidriffs/new.sys
The Markdown output can be pasted straight into a gist, internal wiki or ticket, so the whole team can review it.
Part 3: repos to keep learning
- mytechnotalent/Reverse-Engineering (~15.1k stars): free course covering x86, x64, 32/64-bit ARM, 8-bit AVR and RISC-V.
- guyinatuxedo/nightmare (~3.3k stars): binary exploitation and reversing course built on real CTF challenges.
- wtsxDev/reverse-engineering (~10.8k stars): an "awesome" resource list; last updated in 2023, so some links are stale.
Caveats
- capa and YARA are only as good as their rules; new or heavily obfuscated samples may match nothing.
- FLOSS emulates the sample's code rather than running it natively, but still use it inside an analysis VM.
- Diffing builds from different compilers or optimisation levels yields lots of noise; compare adjacent versions.
How to apply it
- Dev / SOC: Wrap
capa+floss+yr scaninto one triage script that runs on every suspicious file before anyone opens Ghidra. - Tech Lead: When a critical native library ships a security fix, run ghidriff between the two versions and attach the report to the upgrade ticket.
- PM: Automated triage decides within minutes which files need an expert, instead of queueing everything for manual analysis.
Sources & references
- mandiant/capa (GitHub) — mandiant
- mandiant/flare-floss (GitHub) — mandiant
- VirusTotal/yara-x (GitHub) — VirusTotal
- google/bindiff (GitHub) — google
- joxeankoret/diaphora (GitHub) — joxeankoret
- clearbluejar/ghidriff (GitHub) — clearbluejar
- mytechnotalent/Reverse-Engineering (GitHub) — mytechnotalent
- guyinatuxedo/nightmare (GitHub) — guyinatuxedo